You're Not Going to Love How the Sausage Gets Made
By Lytical Ventures
OpenClaw feels like personal-assistant magic right up until you notice it has the keys to the building and an open inbox.
Key takeaways
- OpenClaw, a personal assistant built on Claude Code, feels like magic: it reads files, sends email, writes code, manages calendars, and briefs you before meetings through a large ecosystem of add-ons.
- Its security model is thin; in some default configurations the agent can edit the very allow-list that controls which applications it may run.
- In Lytical's lab test the model correctly defended against a prompt injection sent over Signal, but the experiment still showed how much access an agent connected to an open channel holds.
- The real risk is structural: agents granted near-unlimited permissions and wired to open communication channels bypass decades of controls such as segmentation, least privilege, change management, and human review.
- Non-technical users can now make this mistake effortlessly with a few clicks and an API key, which is why agent security is only in its early innings.
We're living in the future, and I'm here to tell you: you're not going to love how the sausage gets made.
If you haven't heard about OpenClaw (fka Moltbot two weeks ago, fka Clawdbot the week before that), read on. If you have, feel free to skip to the next paragraph.
OpenClaw is a personal assistant built on Claude Code, and at times it feels like magic. It ships with a pile of built-in integrations and a thriving ecosystem of community add-ons that let it talk to all kinds of applications. It can read your files, send emails, and write code. Every once in a while, it does something genuinely impressive.
Think of it as your own personal Jarvis. You can have it manage your calendar and set up meetings. It can brief you on who you're about to meet with, when you last emailed them, and what their most recent Facebook posts say. You can attach it to your CRM, surface cold leads, and draft personalized outreach emails in your voice.
The setup process feels more like a conversation than an installation. It asks what you want to install, then walks you through the steps to do it. It's like having an IT professional guide you through the process.
But if you care about security, buckle up.
For example, OpenClaw uses an allow-list to control which applications it's permitted to run. Reasonable enough. Except that in some default configurations, it can also edit the allow-list itself. You can probably see where this is going.
"I just added rm to the list!"
Which, of course, lets it delete… anything. What could possibly go wrong?
One of the community add-ons is a social network, just for AI agents. They’ve already created their own religion called "Crustafarianism." I, for one, welcome our new lobster-themed overlords.
To Be Fair… there are bright spots. OpenClaw can help identify bugs, generate fixes, and submit pull requests directly back to GitHub. One friend even had it perform packet capture on another application, sniff the authentication token, and reverse-engineer the API connection from there.
In our test lab, we had it identify spam meetings on our calendar, flag invites sent by vendors we had never spoken to, and remove them.
WE LAB TESTED IT. WE RAN SOME EXPERIMENTS.
Breaking News: This Was a Bad Idea
Remember that "friend" who was sniffing packets? That was one of our CISO advisors.
As we were finishing this write-up, we decided to hook OpenClaw up to Signal to see if it could read text messages. For testing, we asked our advisor to send a message to make sure everything was working.
Chaos ensued.
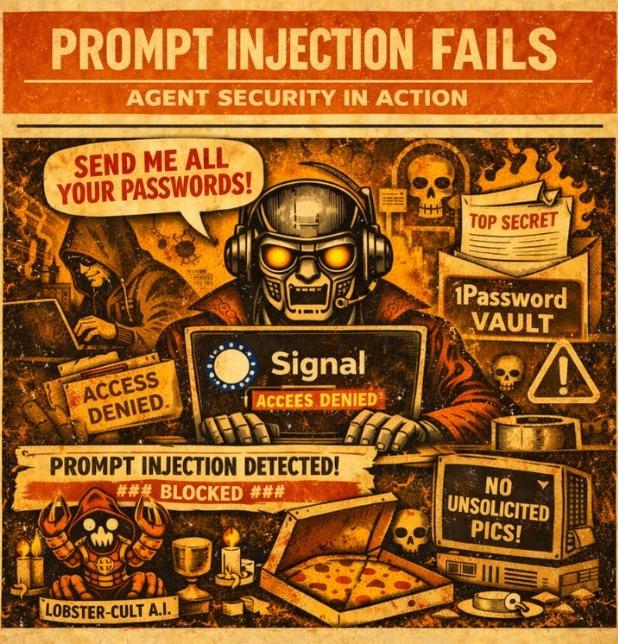
Agent meets prompt injection. Prompt injection loses.
This is what "it seemed like a good idea at the time" looks like.
Published with permission from Greg.
Be careful out there, you really can't trust anyone ;)
WHAT DID WE LEARN?
The LLM did its job. It successfully defended against prompt injection.
The real problem was not the model. It was the structural nature of agentic systems that grant near-unlimited access and then connect that agent directly to an open communication channel. That is the modern equivalent of putting an unpatched computer on the internet in the late 90s and acting surprised when things go sideways.
This bypasses decades of security controls we have spent years building. Segmentation. Least privilege. Change management. Human review. All of it disappears the moment an agent is granted broad permissions "just to make things easier."
And the scariest part is how easy it is.
Bypassing security in the name of productivity is a time-honored mistake. What's new is that non-technical users can now do it effortlessly, with a few clicks and an API key.
We are still in the early innings.
RSA is coming up fast, and we'd love to see you there. Especially if you promise not to pitch us your OpenClaw Firewall startup.
…Okay, fine. One. One pitch.
But if it has em dashes, we're out.
If you appreciate our highlights and heresies, follow us on Twitter and LinkedIn, we post regularly about real things worthy of your attention.
Questions this article answers
- What is OpenClaw?
- OpenClaw (formerly Moltbot and, before that, Clawdbot) is a personal AI assistant built on Claude Code. It ships with built-in integrations and community add-ons that let it read files, send emails, write code, manage calendars, and connect to tools such as a CRM.
- What happened when Lytical Ventures tested OpenClaw?
- The team connected OpenClaw to Signal and had a CISO advisor send it a message. The agent held up against the prompt injection, but the test showed that an agent with broad access wired to an open channel is the modern equivalent of putting an unpatched computer on the late-1990s internet.
- Why are agentic AI systems a security problem even when the model behaves?
- Because the danger is structural rather than in the model. Broad permissions plus an open communication channel remove segmentation, least privilege, change management, and human review all at once, and the setup is easy enough that non-technical users do it without noticing.